<?xml version="1.0" encoding="utf-8"?><feed xmlns="http://www.w3.org/2005/Atom" ><generator uri="https://jekyllrb.com/" version="3.10.0">Jekyll</generator><link href="https://tylabs.com/feed.xml" rel="self" type="application/atom+xml" /><link href="https://tylabs.com/" rel="alternate" type="text/html" /><updated>2026-04-06T14:15:52+00:00</updated><id>https://tylabs.com/feed.xml</id><title type="html">Maldocs and Threat Intelligence Tools</title><subtitle>TyLabs is known for maldocs analysis tools since 2008. Home of QuickSand, Cryptam and PDFExaminer.</subtitle><author><name>TyLabs</name></author><entry><title type="html">QuickSand Serverless in Gcloud</title><link href="https://tylabs.com/blog/gcloud-update/" rel="alternate" type="text/html" title="QuickSand Serverless in Gcloud" /><published>2025-07-17T21:50:00+00:00</published><updated>2025-07-17T21:50:00+00:00</updated><id>https://tylabs.com/blog/gcloud-update</id><content type="html" xml:base="https://tylabs.com/blog/gcloud-update/"><![CDATA[<h2 id="quicksand-now-on-gcp-serverless-malware-analysis-with-cloud-functions-and-storage">Quicksand Now on GCP: Serverless Malware Analysis with Cloud Functions and Storage</h2>

<p>We’re excited to announce a major update for <strong>Quicksand</strong>, our open-source malware analysis tool. Following up on our <a href="https://tylabs.com/blog/maldoc-tools/">original blog post</a>, we’ve now ported Quicksand to <strong>Google Cloud Platform (GCP)</strong>, leveraging the power of <code class="language-plaintext highlighter-rouge">Cloud Functions</code> and <code class="language-plaintext highlighter-rouge">Cloud Storage</code> for a more scalable and efficient threat analysis experience.</p>

<h3 id="the-move-to-serverless">The Move to Serverless</h3>

<p>By moving Quicksand to a serverless architecture on GCP, we’re able to offer a number of key advantages:</p>

<ul>
  <li><strong>Scalability</strong>: <code class="language-plaintext highlighter-rouge">Cloud Functions</code> automatically scale in response to the number of files you need to analyze. Whether you have one document or thousands, Quicksand on GCP can handle the load.</li>
  <li><strong>Cost-Effectiveness</strong>: With a serverless model, you only pay for the compute time you use. This makes Quicksand an even more affordable option for individuals and organizations of all sizes.</li>
  <li><strong>Simplified Workflow</strong>: The new GCP integration streamlines the process of analyzing malicious documents. Simply upload your files to a Google Cloud Storage bucket, and a Cloud Function will automatically trigger a Quicksand scan.</li>
</ul>

<h3 id="how-it-works">How It Works</h3>

<p>The new GCP implementation of Quicksand is designed to be simple and easy to use. Here’s a high-level overview of the workflow:</p>

<ol>
  <li><strong>Upload to Cloud Storage</strong>: Drop your suspected malicious documents into a designated Google Cloud Storage bucket.</li>
  <li><strong>Trigger the Cloud Function</strong>: A Cloud Function is automatically triggered when a new file is uploaded to the bucket.</li>
  <li><strong>Quicksand Analysis</strong>: The Cloud Function executes a Quicksand scan on the uploaded file.</li>
  <li><strong>View the Results</strong>: The analysis results are then stored in another Cloud Storage bucket, where you can easily access and review them.</li>
</ol>

<p>All of the code for the new GCP integration is open-source and available on our <strong><a href="https://github.com/tylabs/quicksand/tree/main/gcloud">GitHub repository</a></strong>. We encourage you to check it out, try it for yourself, and contribute to the project.</p>

<h3 id="get-started-today">Get Started Today</h3>

<p>We’re thrilled to bring the power of Quicksand to the Google Cloud Platform. This new integration makes it easier than ever to analyze malicious documents and gain valuable threat intelligence.</p>

<p>To get started, head over to our GitHub repository and follow the instructions in the README. We’re always looking for feedback, so please don’t hesitate to open an issue or a pull request.</p>

<p>Happy hunting!</p>]]></content><author><name>TyLabs</name></author><category term="blog" /><category term="quicksand" /><category term="maldocs" /><category term="tools" /><summary type="html"><![CDATA[Quicksand Now on GCP: Serverless Malware Analysis with Cloud Functions and Storage]]></summary></entry><entry><title type="html">Cryptam + PDFExaminer = QuickSand</title><link href="https://tylabs.com/blog/maldoc-tools/" rel="alternate" type="text/html" title="Cryptam + PDFExaminer = QuickSand" /><published>2021-07-30T19:34:30+00:00</published><updated>2021-07-30T19:34:30+00:00</updated><id>https://tylabs.com/blog/maldoc-tools</id><content type="html" xml:base="https://tylabs.com/blog/maldoc-tools/"><![CDATA[<p>In 2020, as a pandemic project I rewrote my older QuickSand tool from C into Python and incorporated the features of PDFExaminer into it, dropping the XOR analysis that’s become less common since the early days of document malware. QuickSand allows you to scan within the streams and embedded content of a document or PDF using Yara. QuickSand can also generate similarity hashes for the elements that make up a document, a kind of structural hash.</p>

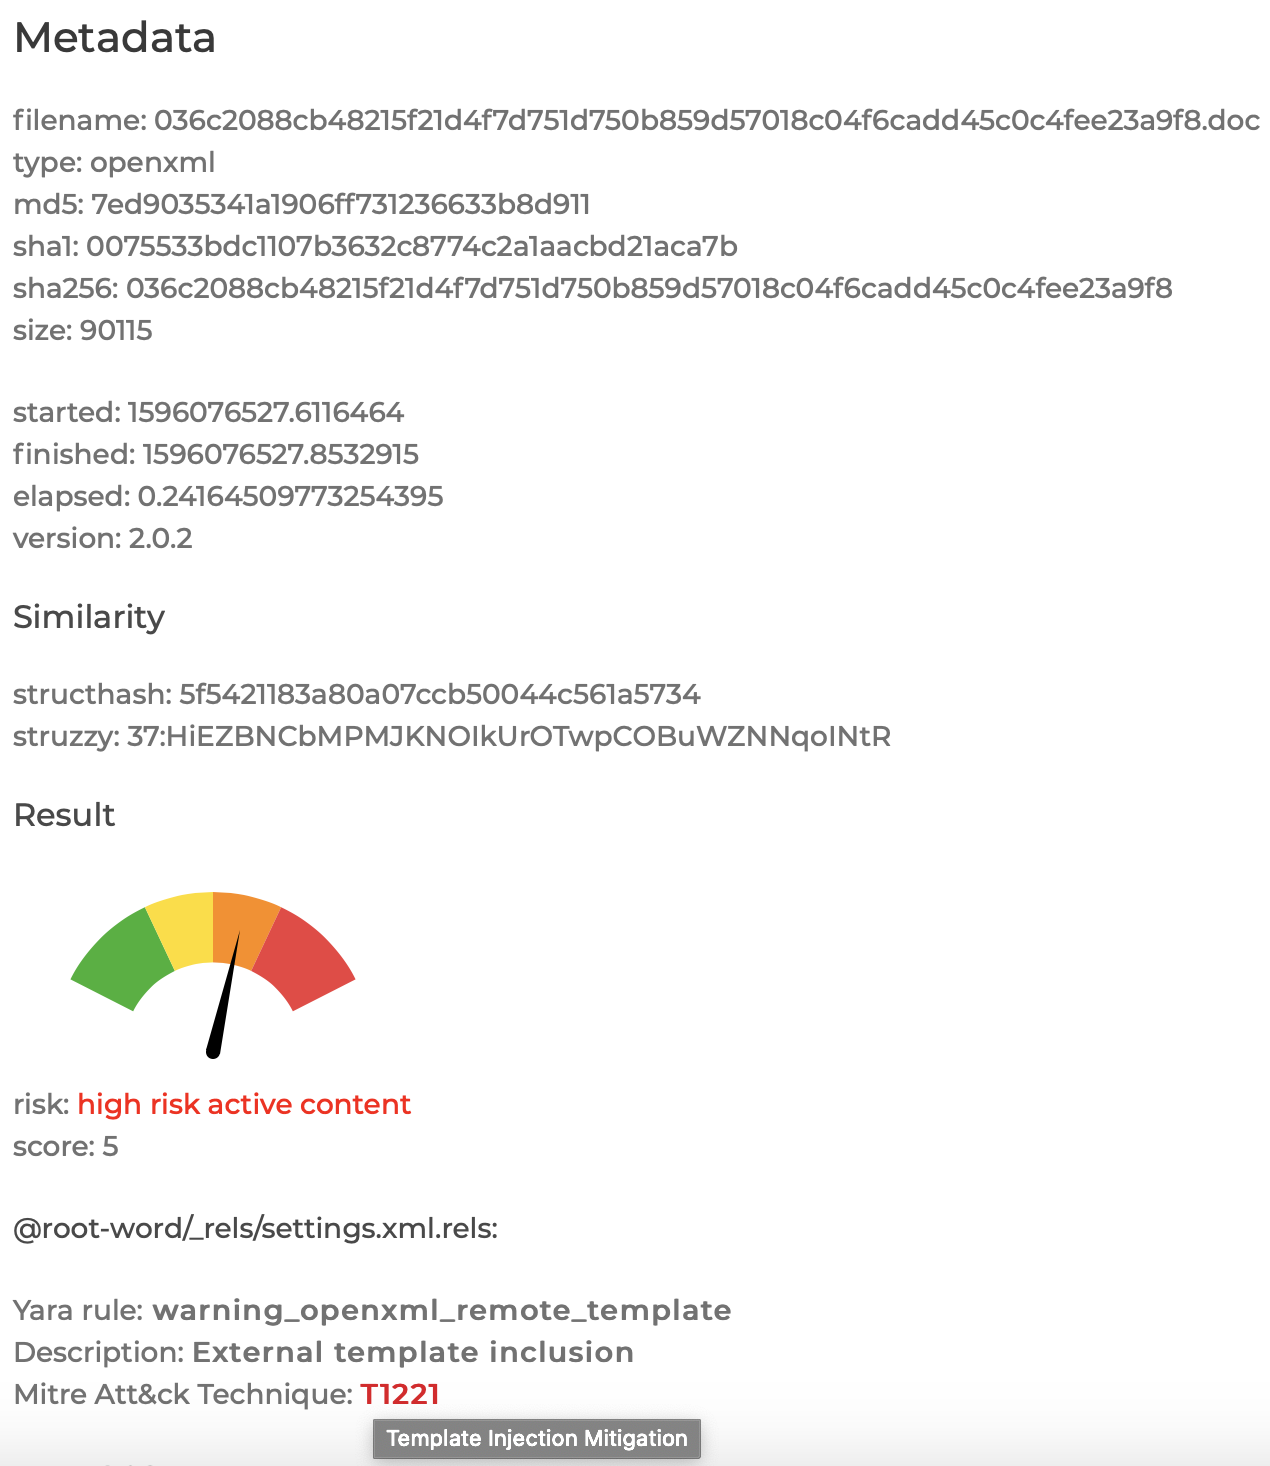
<p>You can use the online demo version at <a href="https://scan.tylabs.com/">scan.tylabs.com</a> running as a serverless AWS Lambda container or <a href="https://github.com/tylabs/quicksand">download the Python code</a> below or use the quicksand command line tool locally <code class="language-plaintext highlighter-rouge">pip3 install quicksand</code>.</p>

<p><img src="/assets/images/riskyscan.png" alt="Example" /></p>

<p>QuickSand is based on the combination of two tools that I originally created in 2009. Cryptam and PDFEXaminer that were designed as PHP web-based malware scanning tools to detect malware in phishing documents. At the time, office documents and PDFs had very low detection in commercial AV. Command-line versions are <a href="/tools/">available</a> in their mostly unmaintained form. <a href="/tools/quicksand/">QuickSand</a> was designed with more of an Analyst focus, automating the extraction of all the streams for further digging while also creating a formal scoring system to present a determination of risk to less technical users.</p>]]></content><author><name>TyLabs</name></author><category term="blog" /><category term="quicksand" /><category term="maldocs" /><category term="tools" /><summary type="html"><![CDATA[In 2020, as a pandemic project I rewrote my older QuickSand tool from C into Python and incorporated the features of PDFExaminer into it, dropping the XOR analysis that’s become less common since the early days of document malware. QuickSand allows you to scan within the streams and embedded content of a document or PDF using Yara. QuickSand can also generate similarity hashes for the elements that make up a document, a kind of structural hash.]]></summary></entry></feed>